mitsec // field · authorized only
FIELD CASES
Yunus Emre Öztaş. Redacted class notes. One featured case on the right. Tape changes the still. Scope map filters the dossier.
● live
clk --:--:--
22 notes
wpsniper
platform · wordpress
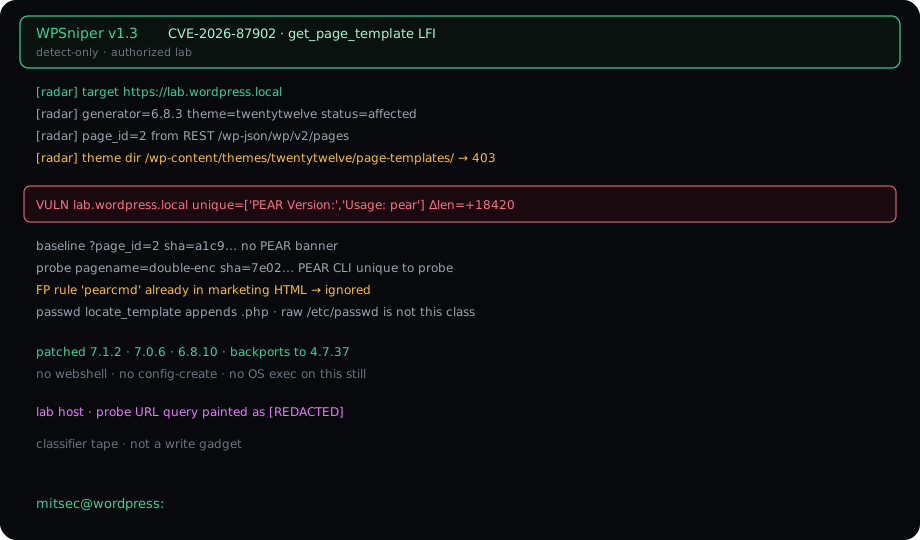
WPSniper — page-template LFI class
CVE-2026-87902. get_page_template include. VULN only on unique PEAR banner. Detect-only. Host stripped.
read the class →Scope map
What surface.
radar // fieldfilter
live--:--:--
androscope · rootless
╭─ AndroSCOPE  · @ynsmroztas
│ target: lab.learn.app
│ mode: rootless mobile pentest
╰ evidence: full

── ASSESS ──
 3  Analyze APK
 4  Static Audit
 5  Exploitability Radar

── RUNTIME ──
 6  Select Module
 7  Shell

mitsec@androscope:
Open the console →
Dossier
Lead, then the stack.
Unauthenticated GitLab file-read
CVE-2026-85706. File.open before auth.
Unclaimed ms-msa scheme
CVE-2026-26123. Scheme emitted, not claimed.
Reset-credentials ATO class
CVE-2026-18963. Email step did not bind.
Empty join key
CVE-2026-82329. Blank join key class.
Provider selection is SQL
Exported provider. Bind args unused.
DEX from a writable path
Loader mapped extract output.